Prompt injection is a serious threat that more teams need to understand, as it can manipulate AI outputs, leak sensitive data, and bypass security controls. By inserting malicious instructions into prompts, attackers exploit how AI models interpret inputs, leading to vulnerabilities. If you don’t address this, your organization risks data breaches and loss of trust. Staying aware of these risks helps you develop better defenses, and there’s more you can uncover to protect your AI systems effectively.

Get business pricing on tech for your team
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Key Takeaways
- Prompt injection can manipulate AI outputs, leading to data leaks and security breaches.
- Recognizing this threat is essential for safeguarding sensitive organizational information.
- Proper input validation and prompt filtering are critical defenses against injection attacks.
- Educating team members about prompt vulnerabilities helps prevent unintentional security lapses.
- Staying updated on prompt injection techniques ensures proactive security measures for AI systems.
As organizations increasingly rely on AI language models, many teams overlook a dangerous vulnerability: prompt injection. This overlooked threat can compromise the integrity of your machine learning systems and jeopardize data security. When you deploy AI models that interpret and generate content based on prompts, malicious actors can manipulate these prompts to influence the model’s output, leading to unintended actions or information leaks. Understanding prompt injection is essential to safeguarding your systems against such exploits.
Prompt injection works by inserting malicious or misleading instructions into the prompts that your AI processes. If your team isn’t aware of this vulnerability, attackers can craft prompts that bypass filters or security measures, causing the AI to perform actions it shouldn’t. For example, an attacker might embed a prompt that instructs the model to reveal confidential data or to execute unauthorized commands. These manipulations exploit the way AI models interpret input, making it critical for your team to develop strategies to detect and prevent such injections. Additionally, the complexity of these prompts underscores the importance of understanding AI prompt vulnerabilities to develop effective defenses.
Malicious prompts can bypass security, causing AI to reveal data or perform unauthorized actions—detect and prevent prompt injection threats.
In the context of machine learning, prompt injection highlights a significant challenge: the models are only as secure as the prompts they receive. If you don’t implement robust input validation and sanitization, you leave your systems open to manipulation. This not only risks exposing sensitive data but also undermines the trustworthiness of your AI solutions. Data security becomes a paramount concern because prompt injection can lead to data breaches, data poisoning, or the integrity of your machine learning models being compromised. Protecting your models from malicious prompts requires a deep understanding of how prompts are crafted and how they can be manipulated.
To defend against prompt injection, you need to adopt a proactive approach. This includes implementing strict input controls, validating user prompts, and employing techniques such as prompt filtering or sandboxing. You should also regularly audit your AI models and their outputs for irregularities that could suggest injection attempts. Educating your team about the nature of prompt injection and its potential risks helps foster a security-first mindset, ensuring everyone understands that even seemingly harmless user inputs can be weaponized. Additionally, understanding the vulnerabilities of AI prompts can help your team develop more effective mitigation strategies.
Ultimately, prompt injection isn’t just a theoretical threat; it’s a tangible risk that can undermine your machine learning initiatives and compromise data security. By recognizing this vulnerability and taking steps to mitigate it, you protect your organization’s AI investments and maintain the trust of your users. As AI continues to evolve, so must your security strategies, making prompt injection awareness an essential part of your overall data security framework.
Products Worth Considering

Apple iPad Air (2025) 13‑inch Wi‑Fi 256 GB – Space Gray (M3 chip)

Bose QuietComfort Headphones (2nd Gen), Wireless Noise-Cancelling Over-Ear Headphones, Black
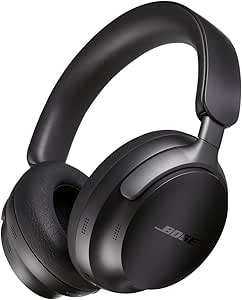
Bose QuietComfort Ultra Wireless Noise-Cancelling Headphones with Spatial Audio, Black
As an affiliate, we earn on qualifying purchases.
Frequently Asked Questions
How Can Organizations Detect Prompt Injection Attempts Early?
You can detect prompt injection attempts early through automated detection systems that monitor unusual input patterns or anomalies in user interactions. Regularly updating these tools helps catch malicious prompts quickly. Additionally, prioritize user education to raise awareness about prompt injection risks, encouraging users to report suspicious activity. Combining automated detection with ongoing training creates a proactive defense, enabling your team to identify and respond to threats before they cause damage.
What Are the Long-Term Implications of Prompt Injection Breaches?
You should understand that prompt injection breaches can have long-term implications, impacting generative ethics and AI accountability. Such breaches may erode trust, cause legal issues, and lead to biased or harmful outputs. By addressing prompt injection risks now, you help guarantee responsible AI use, uphold ethical standards, and maintain accountability. This proactive approach keeps your organization aligned with evolving regulations and promotes sustainable, trustworthy AI development.
Are There Industry-Specific Risks Associated With Prompt Injection?
Ironically, while you’d think prompt injection risks are universal, industry-specific vulnerabilities make them uniquely dangerous. For example, healthcare faces patient data breaches, while finance risks manipulation of transactions. Sector-focused mitigation becomes essential, as generic solutions fall short. You must tailor your defenses, understanding each industry’s nuances. This targeted approach helps prevent breaches that could cause chaos, proving that one-size-fits-all security just isn’t enough in today’s complex landscape.
How Does Prompt Injection Differ From Traditional Cybersecurity Threats?
You should know that prompt injection differs from traditional cybersecurity threats because it exploits AI vulnerabilities through data manipulation, directly targeting the AI’s input layer. Unlike conventional attacks, which often focus on network or system breaches, prompt injection manipulates the AI’s prompts to produce malicious outputs. This makes it essential for your team to understand how data manipulation can compromise AI systems and develop strategies to protect against such vulnerabilities.
What Legal or Ethical Considerations Surround Prompt Injection Vulnerabilities?
You need to take into account legal liabilities and ethical dilemmas when addressing prompt injection vulnerabilities. If you exploit these weaknesses maliciously, you could face legal repercussions for data breaches or unauthorized access. Ethically, you must prioritize user privacy and transparency, avoiding actions that could harm individuals or compromise trust. Proactively, implementing safeguards and adhering to legal standards helps protect your organization and maintains ethical integrity in AI development.
Conclusion
You can’t afford to ignore prompt injection threats—they’re the wolves in sheep’s clothing that can sneak past your defenses. By understanding this risk, you stay one step ahead, preventing potential breaches before they happen. It’s better to address the issue now than to face the music later. Stay vigilant, keep your defenses tight, and don’t let your guard down. After all, an ounce of prevention is worth a pound of cure in today’s digital landscape.