TL;DR

Get business pricing on tech for your team
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Fireworks AI’s November 9 update says attackers accessed account and billing information and, for a limited set of accounts, secrets, datasets and incomplete models. Notion says chat transcripts from its AI Insights feature were in a dataset attackers may have accessed, affecting fewer than 1% of workspaces. The number of affected customers and the fate of accessed data remain unknown.
Fireworks AI said in a November 9 update that an October security incident reached further than the company had initially reported, exposing account and billing information and, for a limited set of accounts, secrets, datasets and incomplete models. Notion separately said chat transcripts from its AI Insights feature were in a dataset attackers may have accessed, with fewer than 1% of workspaces affected, according to the company.
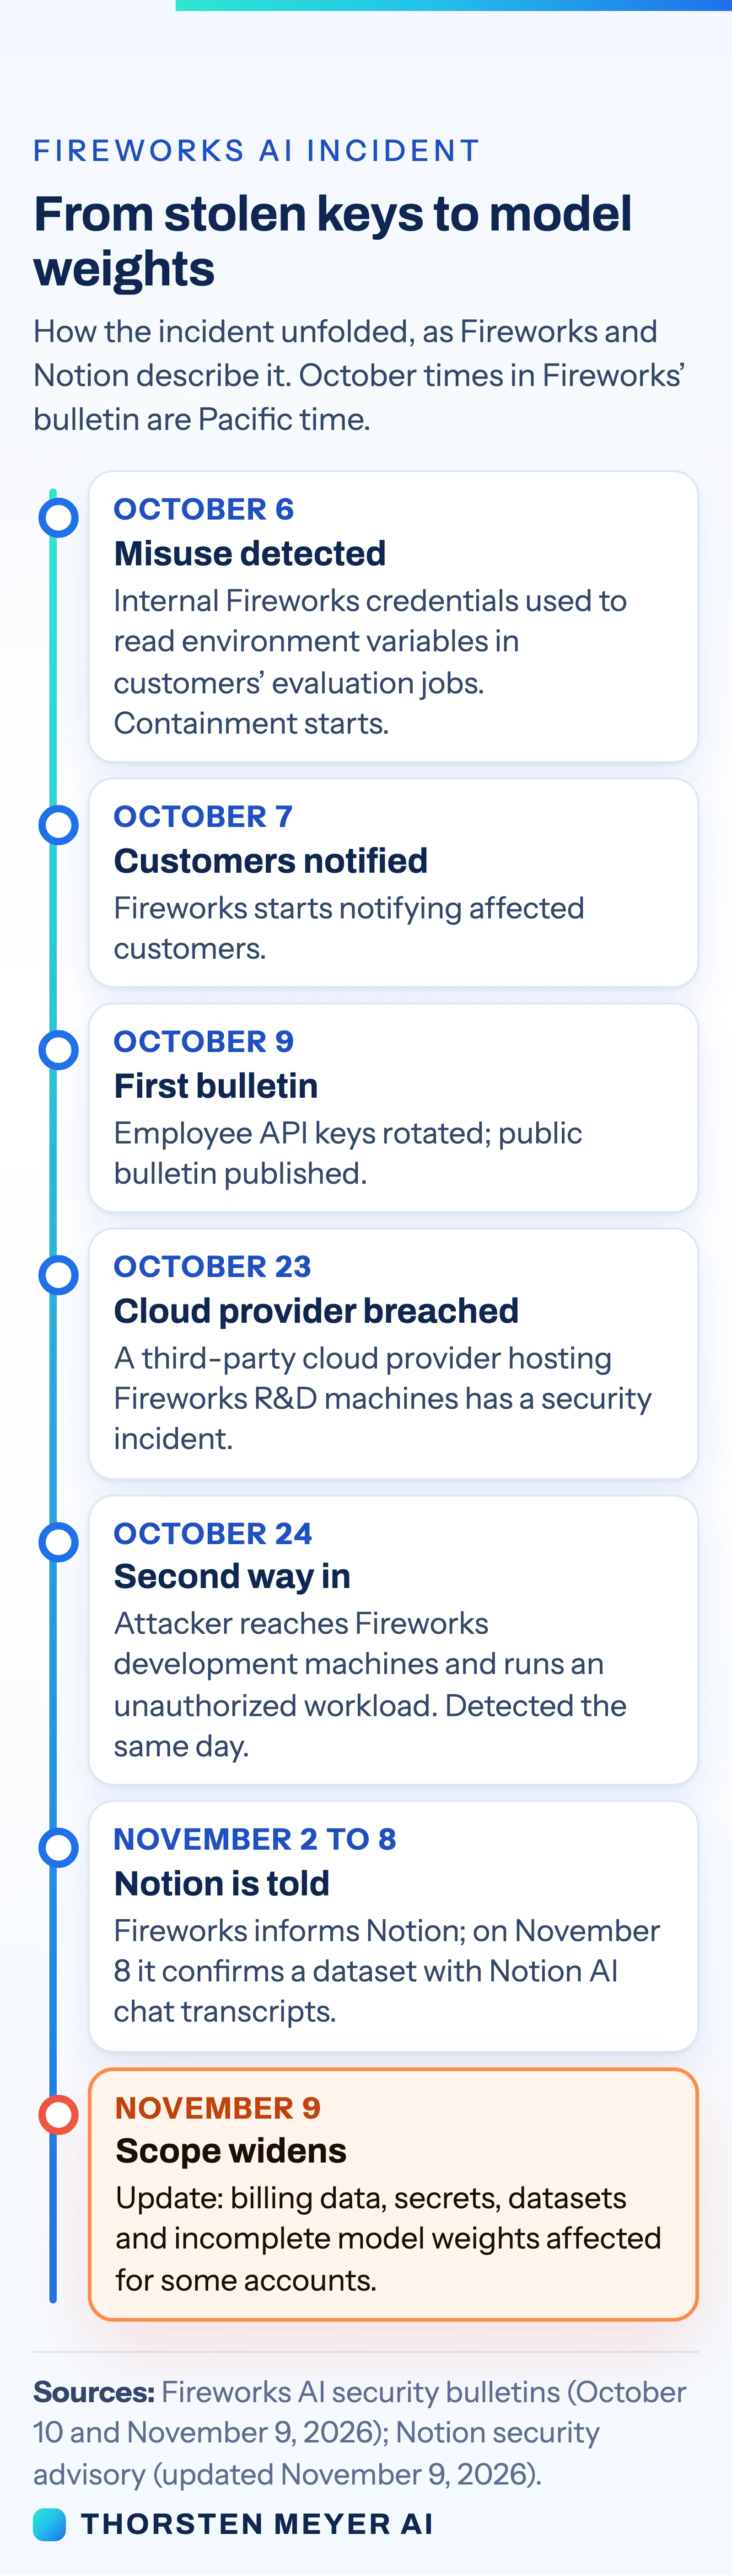
Fireworks’ October 9 bulletin described misuse of internal credentials to read environment variables from a limited number of customer evaluation jobs. Those variables can contain developer settings such as API keys and tokens. At the time, Fireworks said it had not detected unauthorized access to customer models, datasets, training data, inference traffic or personal information. Its November update changed that account: the company said it later discovered impacts to account and billing information, along with access to secrets, datasets and incomplete models for a limited set of accounts.
The company described a second route into its systems. On October 23, a third-party cloud provider hosting Fireworks research and development machines experienced a security incident, according to Fireworks. The next day, an unauthorized party used that access to reach Fireworks development machines and run an unauthorized workload that led to additional customer data impact. Fireworks said it detected this activity on October 24. The company said it has not detected further evidence of successful unauthorized access by the threat actor on the customer platform since October 25.
Fireworks lists exposed information as resource metadata, billing information and, for certain customers, subsets of datasets and incomplete model weights. The billing information includes billing and shipping addresses, invoice and payment history, account balances and credit usage. Fireworks says it does not store payment card numbers and that they were not affected. It also says it has detected no impact to its Inference, Training SDK and Nexus products, which it describes as zero data retention by default.
Risks for AI Platform Customers
The incident matters to companies that use external platforms to train or run AI models because the information involved can include both business account records and customer-provided technical material. Secrets such as API keys or tokens may allow access to connected systems if they remain active, while datasets and model weights can contain commercially sensitive work. Fireworks has not said whether any accessed material was copied, used elsewhere or published.
Notion’s disclosure shows that data associated with a customer-facing AI feature may have been present in a dataset held by a service provider. Notion said fewer than 1% of workspaces were affected and that chat transcripts from Notion AI Insights were in the dataset attackers may have accessed. The statement describes potential access; it does not establish that every transcript was viewed or taken. For organizations using AI vendors, the disclosures make the vendor’s incident scope and the handling of customer data directly relevant to their own exposure reviews.
Products Worth Considering

Bose QuietComfort Headphones (2nd Gen), Wireless Over-Ear Noise-Cancelling Headphones, Black

Sony WH-1000XM5 Premium Noise Cancelling Wireless Headphones – Midnight Blue

Samsung Galaxy Tab A9+ 11-Inch Android Tablet, 64GB, Graphite
As an affiliate, we earn on qualifying purchases.
From Credential Misuse to Broader Access
Fireworks first reported the credential activity on October 9, saying it had identified activity on October 6 and begun containment. It said it started notifying affected customers on October 7, rotated employee API keys on October 9 and later revoked more user API keys and rotated service-account tokens on October 10. The November 9 update came after the company described the separate cloud-provider incident and additional data impact.
Notion said Fireworks contacted it on November 2 about a small dataset that was initially identified as synthetic test data. On November 6, Fireworks told Notion that malicious actors may have accessed potential customer data; the dataset was confirmed on November 8, according to Notion’s account. Fireworks said it notified law enforcement and engaged Palo Alto Networks Unit 42 to conduct forensic work. The timeline reflects the companies’ descriptions of events, not an independently published forensic report.
““For a limited set of accounts, we also discovered impact to secrets, datasets, and incomplete models.””
— Fireworks AI
Scope and Data Use Remain Unknown
Fireworks has not disclosed how many customers were affected or identified the third-party cloud provider. Its update also does not explain how the internal credentials were first obtained, what “incomplete” means for the accessed model weights, or whether attackers retained or used any of the data. The company says its investigation is ongoing and may produce additional information.
Notion’s figure describes the share of workspaces it says were affected, but the available account does not specify how many transcripts were in the dataset or whether attackers accessed particular conversations. Fireworks has said it detected no further successful access to its customer platform after October 25; that statement does not resolve what happened to information accessed earlier.
Customer Reviews and Investigation Updates
Fireworks says its forensic investigation with Palo Alto Networks Unit 42 is continuing and that it notified law enforcement. Customers using the platform can compare the company’s disclosed data categories with the resources and credentials they placed there, and follow any direct notices from Fireworks for account-specific details. The company has not provided a date for a final investigation report.
Further updates from Fireworks or affected customers may clarify the number of accounts involved, the cloud provider’s role and whether accessed data was copied or misused. Until those details are available, the confirmed scope remains the categories and limited subsets described in Fireworks’ November 9 update, alongside Notion’s account of potential access to AI Insights transcripts.
Key Questions
What information does Fireworks say was affected?
Fireworks lists resource metadata and billing information, as well as secrets, datasets and incomplete model weights for a limited set of accounts. It says payment card numbers were not stored and were not affected.
Were Notion AI chat transcripts exposed?
Notion said chat transcripts from its AI Insights feature were in a dataset that attackers may have accessed. The company said fewer than 1% of workspaces were affected; its statement does not establish that every transcript was viewed or copied.
How did attackers reach Fireworks systems?
Fireworks described two routes: misuse of internal credentials to read environment variables from customer evaluation jobs, and later access through a security incident at a third-party cloud provider hosting Fireworks research and development machines.
How many customers were affected?
Fireworks has not disclosed a total number of affected customers. It described the impact to secrets, datasets and incomplete models as applying to a limited set of accounts.
What is known about the stolen data?
The companies have not said whether attackers copied, retained, published or used the accessed information. Fireworks says its investigation is ongoing and may reveal more details.
Source: Thorsten Meyer AI